Agreed scope
Assets, testing windows, limits, and authorization agreed before work begins.
Scoped penetration testing, human validation, and clear results.
Authentication, sessions, access control, and business logic.
View details ↓SERVICE / ↗Authorization, object access, endpoints, and data exposure.
View details ↓SERVICE / ↗Exposed services, configuration, and practical priorities.
View details ↓SERVICE / ↗A focused review with clear decisions for smaller teams.
View details ↓Manual assessment of authorized application workflows, with attention to authentication, session handling, role boundaries, and business logic. Findings are validated and reported with context and reproducible evidence.
Review of authorized REST and GraphQL interfaces, including object-level access, role comparisons, data exposure, and workflow integrity. The test plan reflects available accounts and the agreed scope.
Review of agreed external or internal assets, exposed services, and configurations. Results are prioritized by plausible impact and the work needed to address them.
A focused engagement around the systems and processes most relevant to your business. The report separates immediate fixes from longer-term improvements and gives owners clear next steps.
Assets, testing windows, limits, and authorization agreed before work begins.
Reviewed and explained results, beyond an automated list.
Evidence, impact, contextual severity, and proposed fixes.
Review of improvements as agreed.
Explore a fictional ACME.COM security assessment with a risk overview, coverage, finding IDs, corrective actions, and a retest plan. The assets and results are illustrative; no real ACME.COM system was tested.
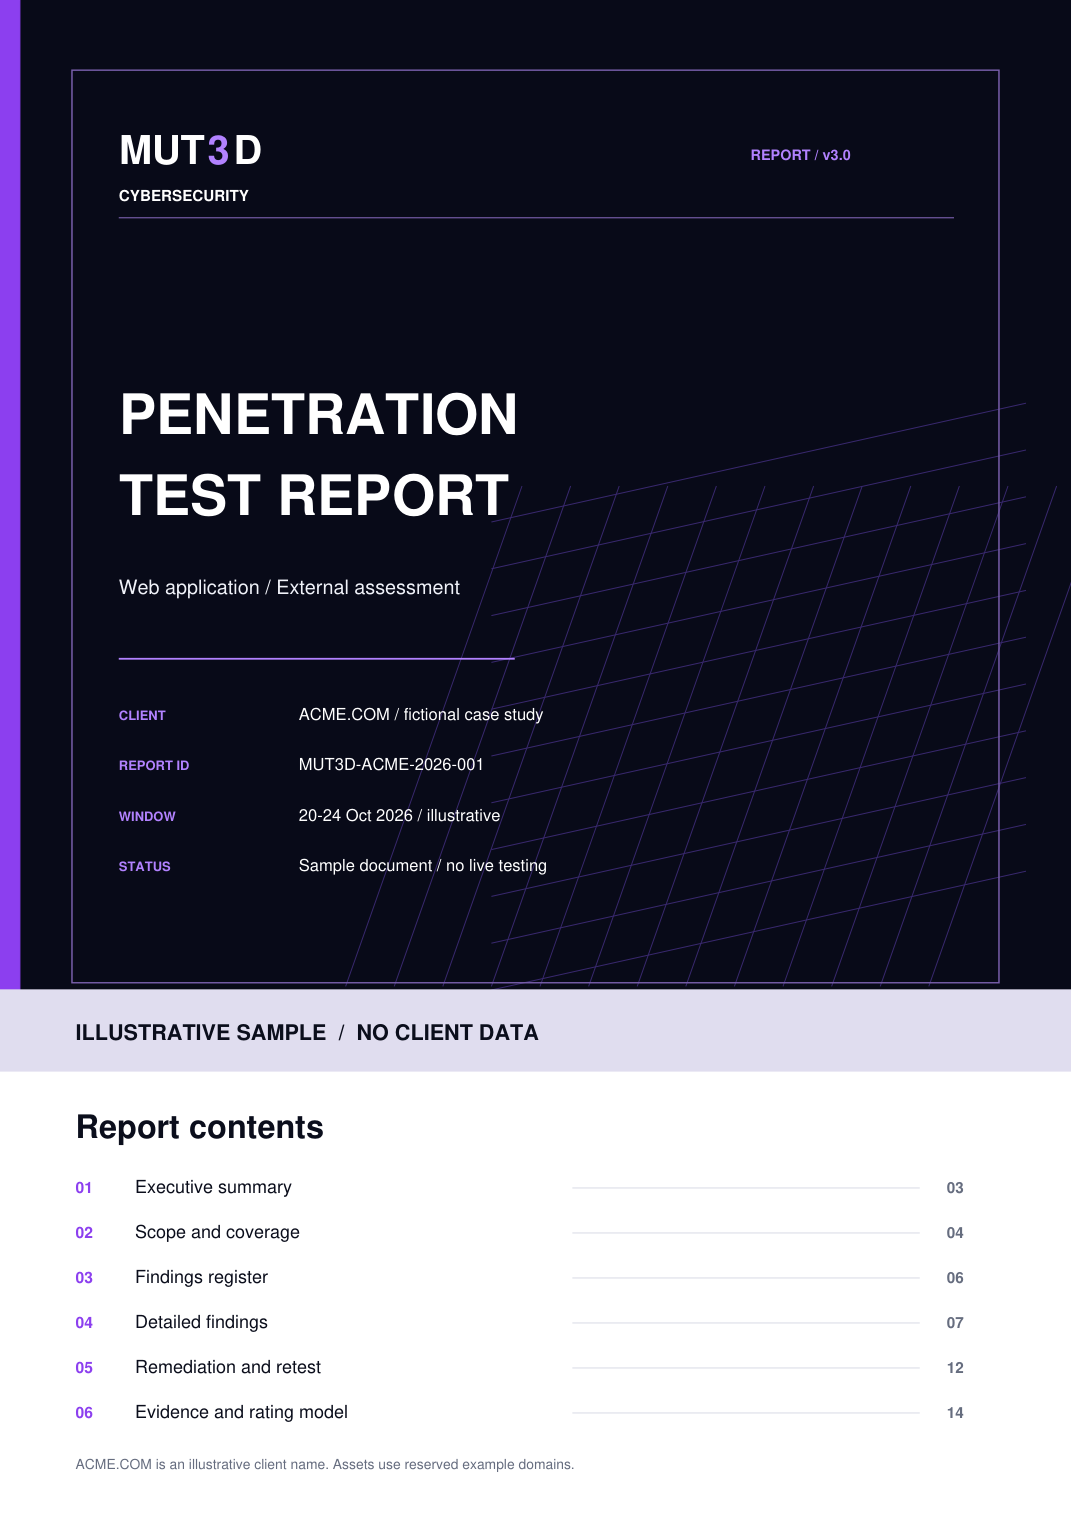
The sample shows how leadership and engineering teams can use the same assessment: clear priorities, traceable evidence, practical remediation, and criteria for closure.
We work to clear objectives and test only with explicit authorization. Tell us what you need reviewed and we can define the next step.
Start a conversation ↗